Skip to content

Currently at TD Bank · Containers, Platform & Cloud Engineering

UmarZaman

Platform & Cloud EngineerKubernetes · Cloud · Compliance

Platform engineer on TD Bank's enterprise container platform, working across AKS and GKE clusters that serve lines of business bank-wide. I work on cluster lifecycle, policy enforcement and AI agent automation that makes compliant cluster provisioning faster — and I contribute upstream to Podman.

Umar Zaman
Toronto, ON
0+

AKS / GKE clusters validated

0%

Infra cost reduced

0%

Deploy time cut

0

Podman PRs merged

Who I am

About

I'm a platform and cloud engineer at TD Bank, on the Containers team inside Platform & Cloud Engineering. I work on Kubernetes cluster operations across AKS and GKE, and I'm currently prototyping AI agents that automate enterprise-compliant cluster provisioning and self-heal pipeline failures for 35+ platform consumer teams.

I spent a term on the security side of the same problem, monitoring compliance posture across 150,000+ hosts and working on Configuration-as-Code compliance for Azure and GCP. That combination is what I like: platform engineering close enough to security that the guardrails are part of the platform rather than bolted on.

~/focus
$ kubectl get focus -o wide
NAME                        STATUS
kubernetes-cluster-lifecyc  Running
policy-enforcement-kspm-an  Running
infrastructure-as-code-and  Running
ai-agent-automation-for-pl  Running
upstream-open-source-in-go  Running
$ 

Where I've worked

Experience

  1. Sept 2026 — Present

    Cloud & DevOps Engineer Intern

    TD Bank Group
    Containers — Platform & Cloud Engineering · Toronto, ON (Hybrid)

    • Researching and prototyping AI agent automation to streamline provisioning of custom-config, enterprise-compliant Kubernetes clusters across 35+ platform consumer teams
    • Designing self-healing deployment agents to auto-resolve pipeline failures, targeting a reduction in cluster provisioning from 1–2 days of manual debugging to a few hours of hands-off background execution
    • Kubernetes
    • AKS
    • GKE
    • AI Agents
    • Automation
    TD Centre - Toronto
    TD Centre - Toronto
  2. May 2026 — Aug 2026

    Cybersecurity Intern

    TD Bank Group
    Security Compliance & Operations Management, Global Security & Defence · Toronto, ON (Hybrid)

    • Monitored security compliance posture across 150,000+ hosts — mainframes, servers and workstations — tracking patch and configuration baselines and triaging non-compliant findings for remediation follow-up
    • Compiled and analyzed compliance reports and data extracts from Splunk dashboards, interpreting threshold breaches to separate systemic non-compliance from noise and delivering defensible reporting up to executive stakeholders
    • Supported Azure and GCP Configuration-as-Code compliance efforts, bridging cloud security policy with enterprise audit and compliance requirements
    • Splunk
    • Azure
    • GCP
    • Configuration-as-Code
    • Compliance
    TD Terrace
    TD Terrace
  3. Jan 2026 — May 2026

    Cloud & DevOps Engineer Intern

    TD Bank Group
    Containers — Platform & Cloud Engineering · Toronto, ON (Hybrid)

    • Validated KSPM policies, STIG controls and security configurations across 10+ AKS and GKE clusters through regression and negative testing, catching enforcement gaps before production promotions and surfacing an untracked STIG compliance gap escalated to engineering leads for remediation
    • Built a Python tool to verify security daemonset deployment across cluster nodes, replacing a manual QA process and adopted as the standard by the platform team
    • Managed Kubernetes cluster lifecycle — provisioning, upgrades and decommissions — across AKS and GKE, deploying Istio ingress and security tooling through Terraform CI/CD pipelines
    • Kubernetes
    • KSPM
    • STIG
    • Istio
    • Terraform
    • Python
    TD Bank Group — Containers — Platform & Cloud Engineering · Toronto, ON (Hybrid)
  4. Jan 2025 — Aug 2025

    Cloud Engineer Intern

    Learning Mode AI
    Toronto, ON (Remote)

    • Built AWS infrastructure from scratch with Terraform for a microservices platform serving 200+ users, reducing infrastructure cost by 40% through right-sized dev and prod environments
    • Set up CI/CD pipelines with GitHub Actions to automate Terraform validation and deployments, reducing deployment time by 70%
    • AWS
    • Terraform
    • GitHub Actions
    • Microservices

No secret about it

Dream Companies

01 / 05

Five companies whose engineering I admire and learn from. For each one, I can point to something I have already built, shipped or merged that connects to the problems they solve.

Simple by design

Everybody I know who uses Wealthsimple loves it, because it makes investing feel simple. More than three million Canadians trust it with over $100 billion in assets. That simplicity is really an infrastructure problem: at TD I run the Kubernetes clusters, Terraform pipelines and compliance controls a regulated platform depends on, and I want to do that work somewhere the complexity stays invisible to the user.

Systems at scale

Tesla exists "to accelerate the world's transition to sustainable energy." Infrastructure where a bad deploy has consequences in the physical world, not just on a dashboard. That is the highest reliability bar I can find, and it's the kind of pressure I want to build under.

Accelerated infrastructure

GPU fleets are the hardest Kubernetes problem going right now — scheduling, node lifecycle and driver-level operations at a scale almost nobody else touches. That is exactly the layer I work at, and I want it at NVIDIA's scale.

IBM

Red Hat · Mainframe

Two separate threads from my work lead straight back here. IBM owns Red Hat, which maintains Podman — where I already have two commits merged. And I've run compliance scanning across mainframes at TD, which is IBM's home turf. This one isn't a stretch; it's a straight line.

GKE · Kubernetes

Kubernetes was born here. I run GKE clusters at a bank every single day, and I want to be on the other side of it — building the platform instead of consuming it. Almost everything I've taught myself points at this door.

Upstream

Open Source

containers/podman — merged
$ git log --author="umar11b" --oneline
29530  view on GitHub
29536  view on GitHub

2 commits merged to main · Go · Red Hat
  • Contributed two merged pull requests to Podman, the upstream OCI container engine, adding --quiet/-q flags to artifact ls and farm list for header-free, scriptable output in CI pipelines
  • Iterated through maintainer code review to add end-to-end test coverage and mutually-exclusive flag validation before merge to main
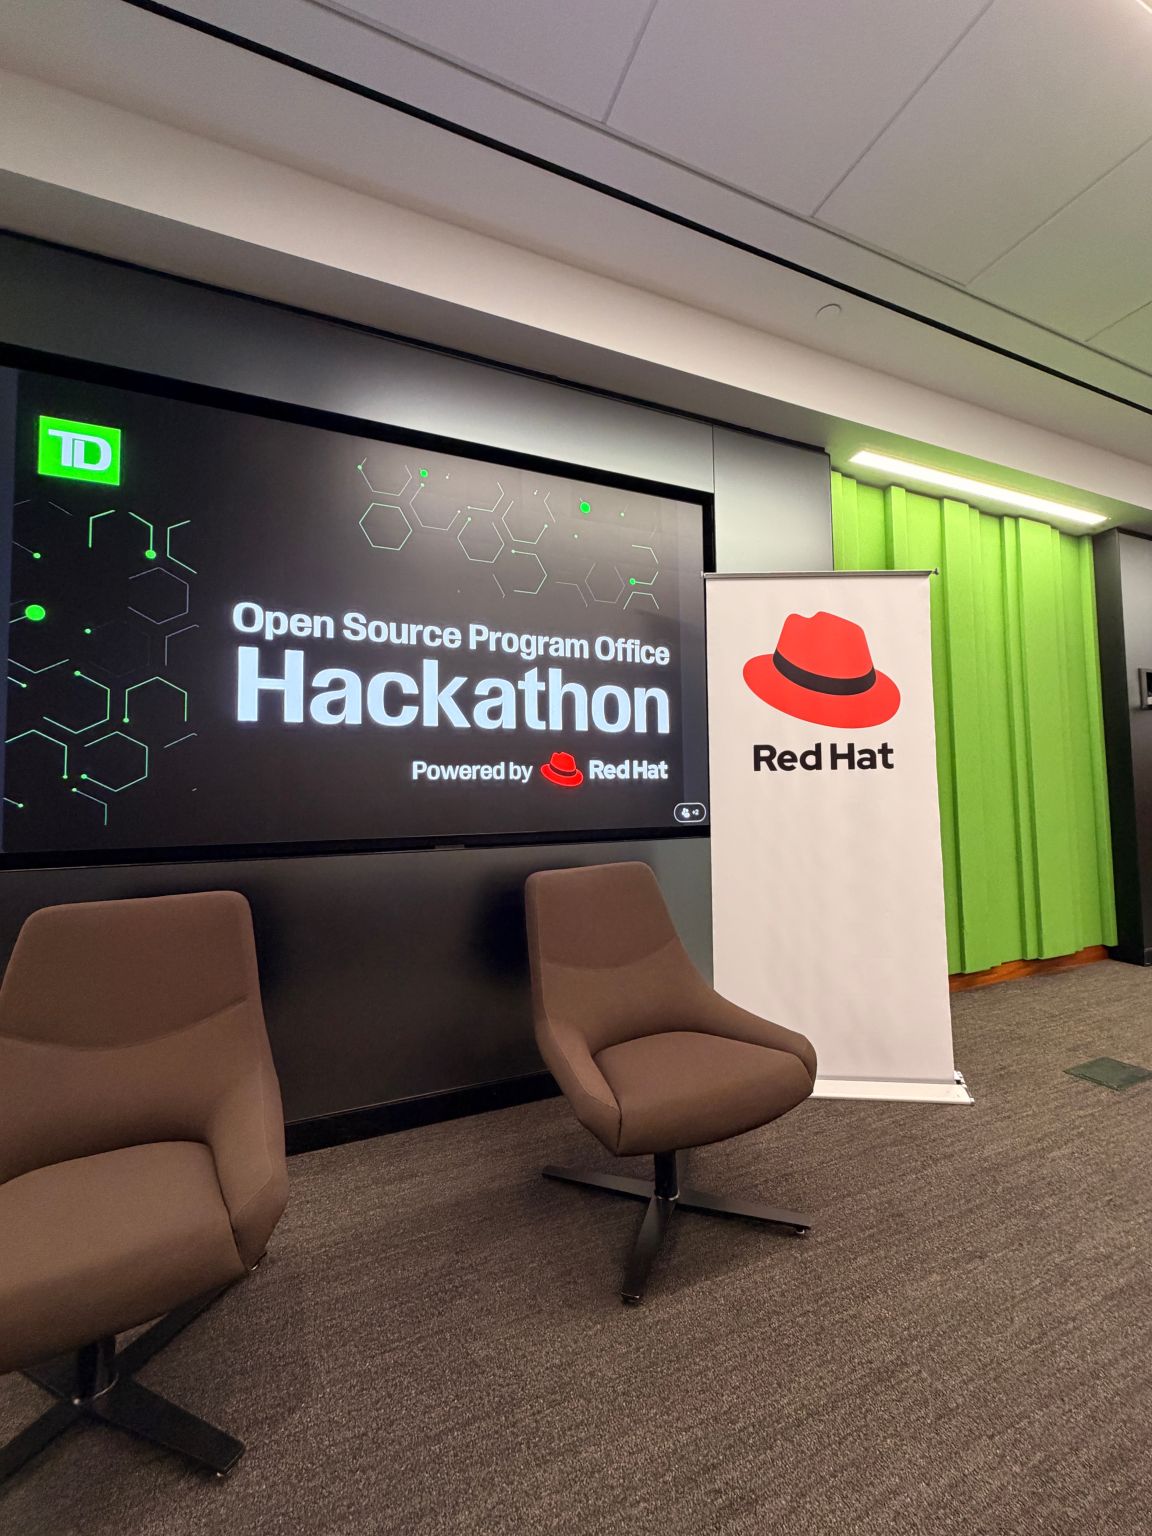
TD Open Source Program Office Hackathon, powered by Red Hat
OSPO Hackathon · Red Hat

Toolkit

Skills

Kubernetes & Containers

  • GKE, AKS, K3s
  • Helm, Istio
  • Docker, Podman
  • GAR, ACR

Cloud & IaC

  • GCP, Azure
  • AWS (EC2, S3, IAM, Lambda)
  • Terraform
  • GitHub Actions

Security & Compliance

  • Wiz
  • KSPM
  • STIG
  • Splunk

Observability

  • Dynatrace
  • Prometheus
  • Grafana
  • CloudWatch

Languages & Systems

  • Python
  • Go
  • Bash
  • Linux (RHEL, Ubuntu)

Certifications

Background

Education

  • Expected 2027

    Sheridan College

    Honours Bachelor of Computer Science (Specialty in Cloud Computing)

    Institute of Technology and Advanced Learning. Taken alongside four consecutive engineering internships.

  • Sept 2020 — Dec 2023

    Sheridan College

    Computer Systems Technology — Software Engineering, Diploma

Get in touch

Contact

Always up for a conversation about Kubernetes, cloud infrastructure, or homelabs.

zamanu@sheridancollege.ca